Free Demo


Convenience for the PDF version
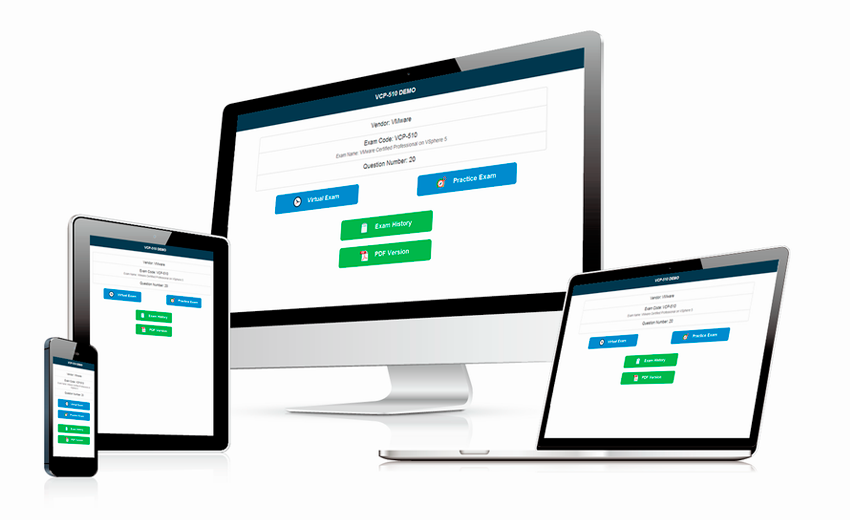
As far as the PDF version of our CAS-003日本語 practice test: CompTIA Advanced Security Practitioner (CASP+) Exam (CAS-003日本語版) is concerned, it has brought us so much convenience concerning the following aspects. First of all, there is demo in the PDF version of CAS-003日本語 exam braindumps, in which the questions are selected from the entire exam files. As a result, customers can have free access to experience whether the exam files are suitable or not. It seems that none study materials can offer such a pre-trying experience except our CAS-003日本語 exam dumps. Aren't you excited about this special advantage? Secondly, the PDF version of our CAS-003日本語 study guide can be printed so that you can make notes on paper for the convenience of your later review. In this way, you can have a lasting memory for what you have learned from our CompTIA CAS-003日本語 dumps torrent. As an old saying goes, the palest ink is better than the best memory. Therefore, the PDF version is undoubtedly an excellent choice for you.
4 Books to Consider When Preparing for CAS-003 Exam
Although there are different ways of studying for certification tests, books remain some of the most helpful resources. CompTIA itself provides its own guide for CAS-003 exam that can be bought on the official website. Also, you can first download the free sample and check if this material meets your needs.
Have you heard about our CAS-003日本語 practice test: CompTIA Advanced Security Practitioner (CASP+) Exam (CAS-003日本語版)? If yes, do you believe the study guide materials files truly live up to their reputation that CompTIA CAS-003日本語 exam braindumps now gain population in the international arena? Of course, it is not so persuasive to just to say without real actions. So I will give you evidence below.

All these topics are neatly organized into 5 domains:
-
Risk management
Under this domain, the candidates should be able to synthesize business and industry influences and understand the related security risks. This requires knowledge of risk management, business models, influencing factors, and more. The applicants also have to have an idea about security and privacy policies, the ability to contrast and compare them, and up-to-date knowledge on policy and process life cycle.
In addition, an understanding of strategies for risk mitigation, security controls, reverse engineering of existing solutions, common business documents, and general privacy principles is needed. The candidates should be able to analyze risk metric scenarios and use that to provide security.
- Enterprise security architecture
This domain will cover various security components, protocols, vulnerabilities, and more. The candidates ought to understand how to analyze a scenario and successfully integrate network and security concepts and architectures while meeting the presented requirements. The knowledge of various physical and virtual network and security devices, applications, and protocol, network designs, etc. is essential.
The applicants should also be able to perform the integration of security controls for the host device while meeting the security requirements. This involves knowledge of trusted OS, security software, host hardening, hardware vulnerabilities. Furthermore, one should have the skills to successfully integrate security controls on mobile devices. Knowledge of enterprise mobility management, rooting, tokenization, etc. is vital for this.
Finally, exam-takers need to be able to choose the appropriate security controls for given vulnerability scenarios. This requires knowledge of various application issues, application security designs, database activity monitoring, firmware vulnerabilities, and more.
- Enterprise security operations
When solving the tasks related to this domain, the candidates are given a scenario where they should successfully conduct an evaluation using various security methods such as malware sandboxing, fingerprinting, pivoting, and such. Knowledge of different network tools is required for analyzing those scenarios and choosing an appropriate tool. Furthermore, the knowledge of e-discovery, data breach, and the various aspects related to that should be used by candidates to implement incident response and execute proper recovery procedures.
- Technical integration of enterprise security
In the fourth domain, the applicants are given a scenario that will test their knowledge of the integration of networks, hosts, storage, and applications to secure enterprise architecture. This requires an understanding of diverse standards, adaption to data flow security, interoperability issues, data security considerations, network secure segmentation and delegation, and such. Moreover, the candidates should be able to integrate cloud and virtualization technologies into secure enterprise architecture using their knowledge of cloud augmented security services, data security, vulnerabilities, and more.
This domain also tests the candidates' ability to integrate and troubleshoot advanced authentication and authorization technologies. This also involves understanding various aspects of attestation, identity proofing, and more. The candidates are required to have an idea about cryptographic techniques as well as the ability to expertly select suitable control to secure communications and collaboration solutions.
- Research, development, and collaboration
To answer the questions under this section, the candidates should perform research whilst applying proper methods and determine industry trends to identify the impact on the enterprise. This requires knowledge of research practices, security implications of business tools, and such. Moreover, implementing security activities across the technology life cycle, which is included in this domain, will be benefited by one's knowledge of system development life cycle, software development life cycle, documentation, etc.
Finally, individuals need to know and explain the importance of interaction across business units to achieve security goals. This includes knowledge of implementation of security requirements, and aspects related to it, among others.
CompTIA CAS-003 is a qualifying exam for the CASP+ certification. This test is designed for the advanced-level cybersecurity practitioners who want to validate their skills and knowledge of risk management, research and collaboration, integration of enterprise security, and enterprise security architecture and operations. The associated certificate is approved by the U.S. DoD to fulfill directive 81.40/8570.01-M prerequisites and complaint with the ISO 17024 standards.
Reference: https://certification.comptia.org/certifications/comptia-advanced-security-practitioner
High pass rate
It is universally acknowledged that everyone yearns for passing the exam in the first time if he/she participates in the exam. However, without CAS-003日本語 training materials, as the exams are varied with different degrees of difficulty, it is not so easy to be always with such good luck. With the guidance of our CAS-003日本語 practice test: CompTIA Advanced Security Practitioner (CASP+) Exam (CAS-003日本語版), you can pass exams without much effort. Upon hearing of it, you may lapse into the doubts. You may wonder whether it is true. At this, I would like to say our CAS-003日本語 exam braindumps enjoy a high pass rate of 98% to 100%, the rate that has never been superseded by anyone else in the field of exam files. Our CAS-003日本語 exam resources have become an incomparable myth with regard to their high pass rate. And that is also why the majority of the sensible people choose our CompTIA CAS-003日本語 best questions rather than others.
No equipment limit for the App version
The App version of our CAS-003日本語 practice test: CompTIA Advanced Security Practitioner (CASP+) Exam (CAS-003日本語版) can be used without limitation on the types of equipment. Whether you use it in your mobile phone or on your computer, it is permissible. What's more, if you don't clear the storage after the first time you have used it, you can look through the exam files of our CAS-003日本語 exam braindumps and do exercises in the offline environment later. That is to say, you do not have to take troubles to download the exam files as long as you have not cancelled them in the first time. Isn't it so convenient to use our App version of our CAS-003日本語 dumps torrent: CompTIA Advanced Security Practitioner (CASP+) Exam (CAS-003日本語版)?
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
CompTIA CASP+ CAS-003 Practice Test Questions, CompTIA CASP+ CAS-003 Exam Practice Test Questions
The CompTIA CAS-003 exam determines if the applicants are advanced in their competency regarding risk management, enterprise security, collaboration, and research. It also checks their capabilities in integrating enterprise security. Passing this test enables you to obtain the CompTIA Advanced Security Practitioner certification, also known as CASP+. Getting it is an indication of bearing advanced skills in risk analysis, security control, technologies for virtualization and Cloud, and cryptographic techniques.
CompTIA CAS-003日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Technical Integration of Enterprise Security | 36% | - Automation and orchestration of security solutions - Secure deployment and integration of security controls - Cryptography and PKI implementation |
| Risk Management | 19% | - Security compliance and policy enforcement - Business continuity and disaster recovery planning - Enterprise risk frameworks and governance |
| Enterprise Security Architecture | 25% | - Secure network and system design - Identity and access management design - Cloud and virtualization security architecture |
| Enterprise Security Operations | 20% | - Monitoring, detection, and incident response - Vulnerability management and threat intelligence |