Free Demo


Convenience for the PDF version
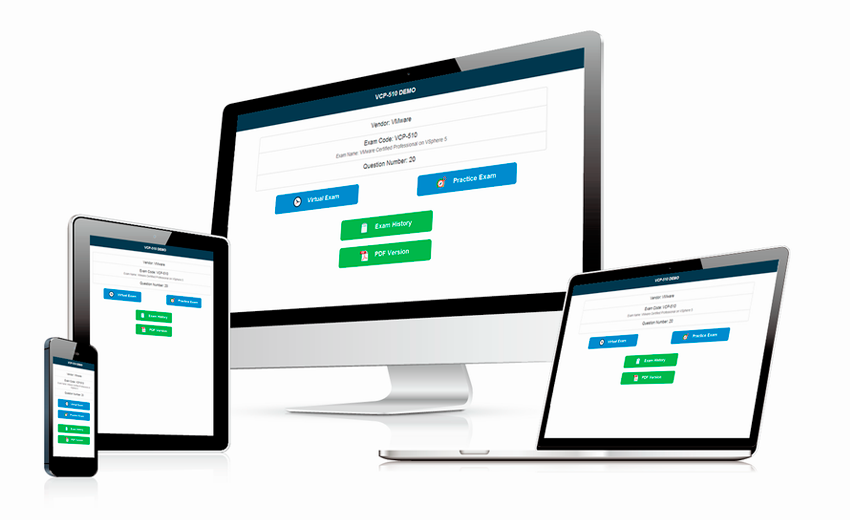
As far as the PDF version of our GWEB practice test: GIAC Certified Web Application Defender is concerned, it has brought us so much convenience concerning the following aspects. First of all, there is demo in the PDF version of GWEB exam braindumps, in which the questions are selected from the entire exam files. As a result, customers can have free access to experience whether the exam files are suitable or not. It seems that none study materials can offer such a pre-trying experience except our GWEB exam dumps. Aren't you excited about this special advantage? Secondly, the PDF version of our GWEB study guide can be printed so that you can make notes on paper for the convenience of your later review. In this way, you can have a lasting memory for what you have learned from our GIAC GWEB dumps torrent. As an old saying goes, the palest ink is better than the best memory. Therefore, the PDF version is undoubtedly an excellent choice for you.
Have you heard about our GWEB practice test: GIAC Certified Web Application Defender? If yes, do you believe the study guide materials files truly live up to their reputation that GIAC GWEB exam braindumps now gain population in the international arena? Of course, it is not so persuasive to just to say without real actions. So I will give you evidence below.

High pass rate
It is universally acknowledged that everyone yearns for passing the exam in the first time if he/she participates in the exam. However, without GWEB training materials, as the exams are varied with different degrees of difficulty, it is not so easy to be always with such good luck. With the guidance of our GWEB practice test: GIAC Certified Web Application Defender, you can pass exams without much effort. Upon hearing of it, you may lapse into the doubts. You may wonder whether it is true. At this, I would like to say our GWEB exam braindumps enjoy a high pass rate of 98% to 100%, the rate that has never been superseded by anyone else in the field of exam files. Our GWEB exam resources have become an incomparable myth with regard to their high pass rate. And that is also why the majority of the sensible people choose our GIAC GWEB best questions rather than others.
No equipment limit for the App version
The App version of our GWEB practice test: GIAC Certified Web Application Defender can be used without limitation on the types of equipment. Whether you use it in your mobile phone or on your computer, it is permissible. What's more, if you don't clear the storage after the first time you have used it, you can look through the exam files of our GWEB exam braindumps and do exercises in the offline environment later. That is to say, you do not have to take troubles to download the exam files as long as you have not cancelled them in the first time. Isn't it so convenient to use our App version of our GWEB dumps torrent: GIAC Certified Web Application Defender?
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
GIAC GWEB Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Topic 1: Authentication and Session Management | - Session tokens and cookie security - Password storage and hashing mechanisms - Multi-factor authentication concepts |
| Topic 2: Web Application Defense and Mitigation | - Incident detection and response basics - Logging and monitoring strategies - Web application firewalls (WAF) |
| Topic 3: Web Application Architecture & Fundamentals | - Client-server model and web components - Web application lifecycle basics - HTTP/HTTPS protocol behavior |
| Topic 4: Browser and Client-Side Security | - Same-Origin Policy (SOP) - Content Security Policy (CSP) - Security headers and browser protections |
| Topic 5: Secure Web Application Design | - Input validation and output encoding - Least privilege and access control design - Secure coding practices |
| Topic 6: Web Application Vulnerabilities | - Cross-Site Request Forgery (CSRF) - Insecure direct object references (IDOR) - Injection attacks (SQL, command, LDAP) - Cross-Site Scripting (XSS) |
GIAC Certified Web Application Defender Sample Questions:
What are the best practices for securing session management in web applications?
(Choose two)
Response:
- A. Storing session tokens in local storage
- B. Using long, unpredictable session tokens
- C. Setting session expiration times
- D. Allowing session tokens to be transmitted via URL
Correct Answer: B,C 🗳️
AJAX calls can be vulnerable to interception and manipulation. Which of the following is an effective countermeasure to secure AJAX calls?
Response:
- A. Using simple HTTP authentication for AJAX requests
- B. Employing GET requests for transferring sensitive information
- C. Implementing strong session management with secure tokens
- D. Allowing cross-origin requests without restrictions
Correct Answer: C 🗳️
What is the primary role of a reverse proxy in a web application architecture?
Response:
- A. To distribute load among several servers.
- B. To act as an intermediary for requests from clients seeking resources from servers.
- C. To provide additional compute resources to a server.
- D. To encrypt outgoing server responses.
Correct Answer: B 🗳️
Which techniques can help mitigate CSRF attacks?
(Choose two)
Response:
- A. Restricting GET requests for sensitive actions
- B. Using anti-CSRF tokens in forms and URLs
- C. Implementing session timeout for all users
- D. Limiting session IDs to trusted domains
Correct Answer: B,D 🗳️
When is it appropriate to use encryption over tokenization for protecting sensitive data?
Response:
- A. When the data needs to be processed or analyzed
- B. When there is no requirement for direct data retrieval
- C. When replacing data with a token suffices for processing
- D. When minimal changes to the existing system are preferred
Correct Answer: A 🗳️